
Shadow
AI
 BY THE NUMBERS
AI is Supercharging Enterprise Mobile Attacks
76% of security teams can't keep up with the pace of AI-driven attacks
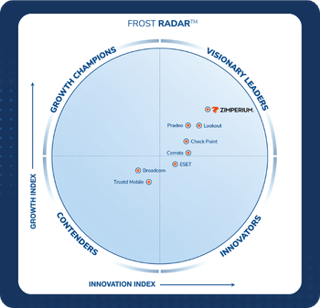
Frost & Sullivan's 2026 Frost Radar™ for Mobile Threat Defense
Leader and Strongest Performer in Innovation and Growth
Zimperium has been named as a Visionary Leader in Frost & Sullivan's 2026 Frost Radar™ for Mobile Threat Defense (MTD).
Frost & Sullivan identified Zimperium as the strongest performer on both the Innovation Index and Growth Index, recognizing our continued leadership in protecting enterprises and government organizations against the rapidly evolving mobile threat landscape.

Real-time Threat Visibility
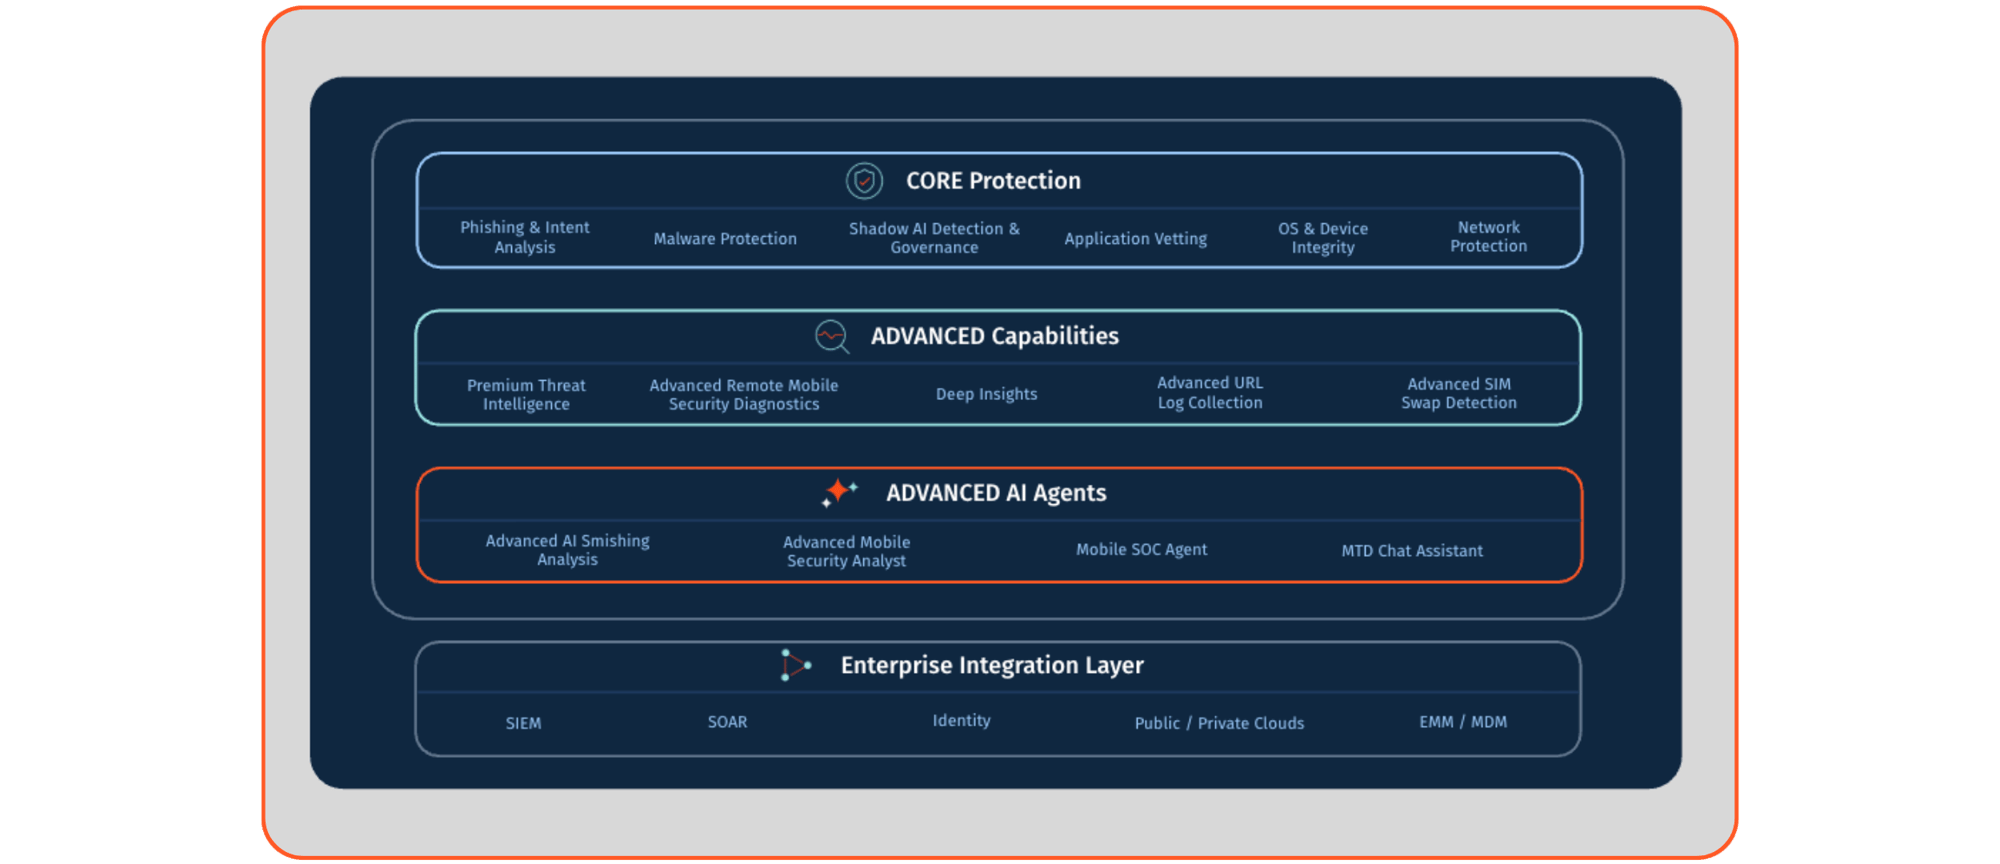
Centralized visibility across your mobile fleet, detecting phishing, malware, network, and app risk, attacks, with critical forensics.

Continuous App Vetting
Automatic vetting of every app on an employee device, flagging risk, shadow AI, non-compliant and malicious apps before they become the entry point.

On-Device Mobile Protection
Block phishing, malware, unsafe networks, and malicious apps in real time, empowered by AI on the device even when offline.

Automated AI SOC Analysis
Correlate mobile threat events into a single incident, confirm it's real, and deliver response guidance, so SOC analysts can act with confidence.

Robust
NG-SIEM Integration
Push threat forensics and correlated incident data directly into your CrowdStrike Next-Gen SIEM in real time.
Explore Related Content

Prevent Malicious Mobile Apps from Taking Over

Mobile Threat Defense

App Vetting - Your First Line of Defense